
 VoIP
 Blog
 Business Communication
 Customer Experience
 Leadership
 Marketing & Sales
 Nextiva News
 Productivity
STIR/SHAKEN is a caller ID authentication framework that helps phone providers check whether a caller is allowed to use the number shown on an incoming call. It uses digital signatures to help detect fake caller IDs, but it does not guarantee that a call is safe or stop every robocall.
If you’ve ever ignored an unfamiliar number, you know how hard it can be to trust caller ID. Your customers face the same choice when your business calls them. STIR/SHAKEN gives VoIP service providers and mobile carriers a way to check caller ID details, though even verified calls can receive spam labels.
Understanding why starts with how authentication works. This guide explains the process, what the attestation levels mean, and what to check with your phone provider if your business calls are being flagged.
What Is STIR/SHAKEN?
STIR/SHAKEN is a set of standards that lets phone providers sign and verify caller ID information on IP-based calls. It helps the receiving provider assess the number presented with a call, rather than simply accepting it at face value.
STIR: Secure Telephone Identity Revisited.
SHAKEN: Signature-based Handling of Asserted Information Using toKENs.
STIR defines the underlying authentication protocols. SHAKEN provides a framework for applying them across telephone service provider networks.
Background: Why caller ID needs authentication
Traditional caller ID does not, by itself, prove that someone has permission to use the displayed number. Scammers can exploit that weakness to make calls appear to come from a bank, government agency, or local business.
Authentication adds a way for providers to check signed calling information. The FCC has expanded its use through rules implementing the TRACED Act, but authentication remains one part of the wider effort to address illegal robocalls.
How Does STIR SHAKEN Call Authentication Work?
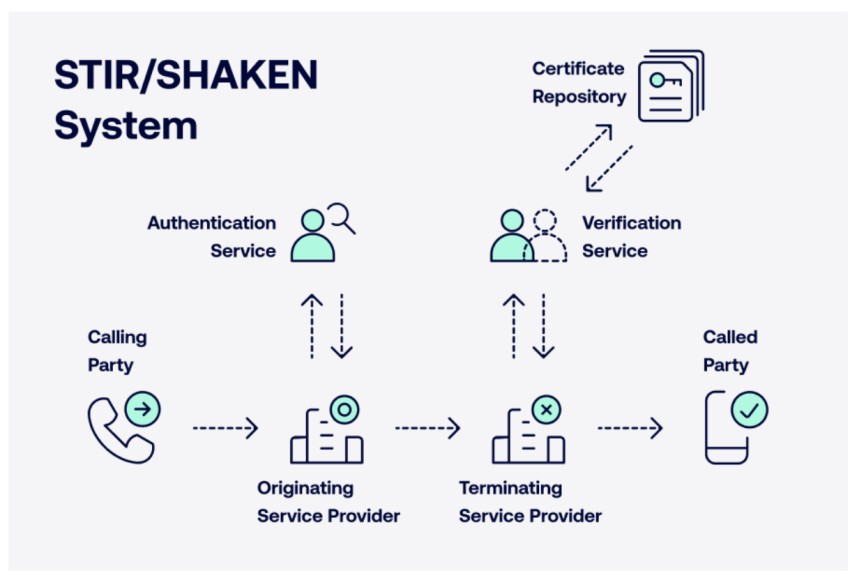
STIR/SHAKEN call authentication works by having the originating provider digitally sign calling information and the receiving provider verify it. The receiving provider then uses the authentication result alongside its call analytics to decide how to handle the call.
Step 1: The originating provider signs the call
When you initiate a call, your provider assesses what it knows about your business and your authorization to use the calling number. It uses that information to assign an attestation level.
The provider creates a digitally signed token using its private key and includes it in the SIP Identity header. That header travels with the SIP INVITE through supported networks toward the receiving provider.
Step 2: The receiving provider verifies the signature
The receiving provider’s verification service checks the digital signature using the signing provider’s certificate. It also checks the certificate’s trustworthiness and whether the signed information matches the call.
Successful verification confirms the signed calling information. It does not prove that the caller’s intentions are legitimate or guarantee that the call will reach the recipient.
Step 3: Call analytics guide the outcome
The receiving provider considers authentication results alongside other signals, such as calling patterns and number reputation. Depending on its systems and policies, it may deliver the call, display a warning, or block it.
Even a fully authenticated business call can receive a spam label. If this happens to your calls, collect examples with the calling number, destination, date, and time, then ask your provider to investigate.
The three STIR/SHAKEN attestation levels
The signing provider assigns an attestation level based on what it can verify about the caller and their authorization to use the calling number. The receiving provider can use this information alongside other signals when deciding how to handle the call.
| Attestation level | What the provider verifies |
|---|---|
| A: Full | The provider knows the customer and has verified their authorization to use the calling number. |
| B: Partial | The provider knows the customer but cannot verify their authorization to use the calling number. |
| C: Gateway | The provider identifies where the call entered its network but cannot authenticate the original caller. |
A-level attestation provides the strongest assurance about the caller’s authorization to use the number. However, it does not prove that the call is safe or guarantee delivery.
What to do if your calls receive lower attestation
Ask your provider what attestation levels your outbound calls receive and whether it has verified your authorization to use each number. This is especially useful if your business uses numbers held with another provider or places calls through a separate dialer.
B- or C-level attestation does not automatically mean a call is spam. Your provider can help determine whether the level reflects missing authorization information, the call’s network path, or another limitation.
Why Some Calls Cannot Be Verified
A call needs a supported network path for its authentication information to reach the receiving provider. Legacy non-IP network segments can interrupt that path. International calls and calls crossing networks with different authentication capabilities can also have verification gaps.
An unverified call is not necessarily a scam. Likewise, a signed call can still carry an unwanted sales pitch or fraudulent request. Authentication checks calling information; it does not evaluate everything a caller says.
Treat any verification indicator as one signal. If someone requests a payment, password, or one-time code, verify the request through a contact method you already trust.
Types of Scam Calls STIR/SHAKEN Can Mitigate
STIR/SHAKEN helps providers detect suspicious caller ID information associated with several common scams. It makes impersonation through spoofed numbers harder, but it cannot prevent every fraudulent call.
1. Phishing and vishing
Threat actors pose as genuine sources such as banks, credit card companies, or government agencies to trick victims into revealing personal information. They can try to get victims to reveal one-time passwords and other details that can compromise their identity.
Vishing is short for “voice phishing.” Attackers trick targets into giving out sensitive information by impersonating a legitimate professional. They try to retrieve personal information or receive financial payments.
STIR/SHAKEN can help providers identify suspicious calling information used in these attempts. It cannot stop a scammer from making a fraudulent request using a number they are authorized to use.
2. Tech support scams
Many threat actors impersonate a company’s tech support staff to convince victims of malware in their system. They encourage targets to update the software. While updating, the victim innocently gives away remote access to their computer.
Attackers use this access to get the victim’s personal information. Sometimes, they may install malware or ransomware on the victim’s computer.
Call authentication can help when these attackers spoof a company’s number. It does not verify their technical advice or make remote access safe.
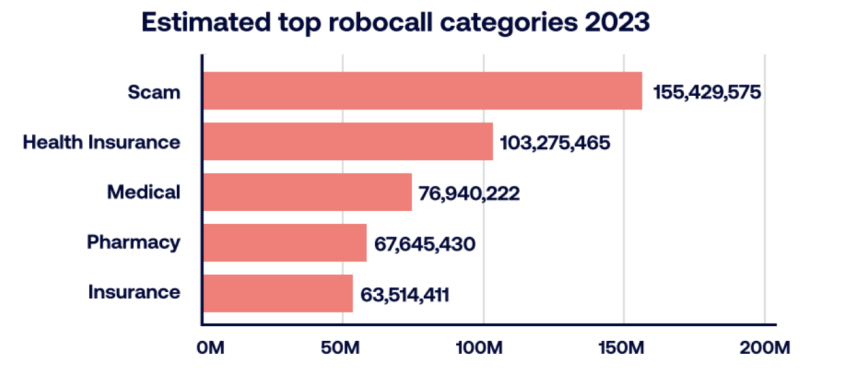
3. Illegal robocalls
Robocalls use prerecorded messages, and some serve legitimate purposes, such as alerts and reminders. Whether a particular call is lawful depends on the applicable rules and circumstances, including consent where required.
However, some unwanted robocalls come from scammers who engage victims with fake notices such as, “You have violated a traffic law; pay $X in fines to avoid full-scale legal inquiry.”
When attackers spoof the caller ID, it becomes tricky for victims to identify and block such calls. Authentication gives providers another signal to use alongside their robocall detection tools.
Benefits of STIR/SHAKEN
STIR/SHAKEN gives providers more information to assess calls. Here are some of its notable benefits:
- Supports spam detection: Providers can use authentication results alongside call analytics to assess suspicious traffic.
- Makes caller ID more useful: Verification indicators can help recipients assess incoming calls where their network and device support them.
- Supports fraud prevention: Detecting suspicious calling information can help providers address impersonation attempts.
- Helps investigate suspicious traffic: Signed call information includes an origination identifier that can support traceback investigations.
Why You Should Use Authenticated Numbers for Outbound Dialing
Customers may hesitate to answer an unfamiliar number. Authenticating your outbound business phone numbers gives receiving providers more information to assess your calls and can support verification indicators where available.
Help customers recognize your business
Authenticated calling information can give customers more confidence when deciding whether to answer. Where supported, a verification indicator shows that the call’s number has passed authentication checks, helping customers assess unfamiliar calls from your business.
Support better call answer rates
Customers who feel more confident about an incoming call may be more willing to answer. Authentication can support that confidence, but its effect on answer rates depends on the recipient, the caller ID display, and your number’s reputation. Even fully authenticated calls can receive spam labels or go unanswered.
Enhanced brand reputation
Accurate, authenticated calling information can support your business’s credibility during sales calls, appointment reminders, and customer service callbacks. A consistent calling identity supports your brand reputation, while inaccurate caller ID details can create confusion and weaken customer trust.
Compliance with regulations
Using numbers your business is authorized to present supports your provider’s caller ID authentication process. Under FCC rules implementing the TRACED Act, covered providers generally must authenticate calls on their IP networks, subject to applicable exceptions.
Authentication does not make an outbound calling campaign compliant on its own. Your business must still follow applicable consent, telemarketing, and do-not-call requirements.
STIR/SHAKEN Implementation and Requirements in 2026
Phone providers handle the certificates and systems needed to sign and verify calls. Most businesses work with their provider to confirm their outbound numbers and provide proof that they are authorized to use them.
Is STIR/SHAKEN mandatory?
FCC rules generally require covered providers to implement STIR/SHAKEN in the IP portions of their networks, subject to applicable extensions and exemptions.
The initial deadline was June 30, 2021. Later deadlines included June 30, 2022, for certain small providers and June 30, 2023, for facilities-based small providers and covered gateway providers. See the FCC’s implementation announcement.
Providers also have Robocall Mitigation Database filing obligations. These filing requirements apply to providers, rather than every business that uses their phone services.
The FCC’s third-party authentication rules, effective September 18, 2025, clarify provider accountability. A provider using a third party to sign calls must still make the attestation decisions and use its own certificate.
What your business should do
- Confirm your outbound numbers. List every number used by your phone system, dialer, and contact center.
- Provide authorization documents. Ask your provider what it needs to verify numbers held elsewhere.
- Check your calling setup. Confirm how authentication works when calls move between connected services.
- Investigate delivery issues. Save the calling number, destination, date, and time for examples of blocked or mislabeled calls.
- Keep your records accurate. Update your provider when your business details or authorized numbers change.
For example, Nextiva requires proof of authorization when customers want to present an outbound number that was not purchased from or ported to Nextiva. Its support guidance lists a recent phone bill or a letter of authorization from the number owner as possible proof.
How STIR/SHAKEN Relates to Rich Call Data (RCD)
Rich Call Data, or RCD, adds details such as the business name, logo, or reason for calling to supported incoming-call displays. STIR/SHAKEN helps authenticate calling information; RCD adds context so recipients can better understand who is calling and why.
The IETF published RFC 9795 in July 2025 to define how rich call information can be digitally signed and protected against alteration.
RCD is not automatically included with every authenticated call. What a customer sees depends on support across the calling service, receiving network, and device. Ask your provider about availability before promising branded caller information to customers.
How STIR/SHAKEN and 10DLC Work Together
10-digit Long Codes (10DLC) are local long code numbers. STIR/SHAKEN and A2P 10DLC apply to different parts of business communication. STIR/SHAKEN helps providers authenticate voice caller ID information. A2P 10DLC registration identifies businesses and messaging campaigns that send application-to-person texts through U.S. local 10-digit numbers.
If your business calls and texts customers, work with your provider to complete the relevant processes for each channel. Registering messaging campaigns does not authenticate voice calls, and verifying outbound calling numbers does not complete messaging registration.
Neither process guarantees delivery or replaces applicable consent requirements.
Nextiva’s Business Phone System Solution
Putting call authentication into practice starts with verifying the numbers your business uses. Nextiva requires proof of authorization for outbound caller ID numbers that were not purchased from or ported to its service.
Start with the Nextiva Business Phone System and ask the team to review your outbound numbers and explain how authentication applies to your setup.
Put call authentication into practice with Nextiva
Get the Nextiva Business Phone System and work with our team to verify your outbound caller IDs.
Frequently Asked Questions About STIR/SHAKEN
Ask your phone provider for signing records and attestation values for recent calls, where available. Share the calling number, destination, date, and time so it can investigate specific examples. A verification badge or spam label alone does not confirm how a call was signed or verified.
Ask your provider to investigate authentication results, number reputation, and call routing. Full attestation confirms your provider’s knowledge of the caller and authorization to use the number, but it does not guarantee delivery or prevent spam labels. Provide examples of affected calls to help identify the cause.
Yes, calls using toll-free numbers can be authenticated through STIR/SHAKEN. Ask your provider how it verifies your authorization to use the toll-free number and what attestation level it assigns to those outbound calls. Authentication does not guarantee a particular caller ID display or delivery outcome.
Transfers and forwarding can change call information or introduce additional providers into the call path, which can affect verification. Ask your provider how it handles authentication for transferred and forwarded calls, especially when your phone system and contact center use different services.
Requirements vary by provider. You may need business identity details and proof that you are authorized to use the calling number, such as a recent phone bill or a letter of authorization. Ask your provider which documents it accepts, particularly for numbers held with another service.
International calls may cross networks that handle authentication differently, so verification information may not reach the receiving provider intact. Ask your provider how it handles authentication on U.S.-bound routes and what information it needs to verify your outbound numbers. An unverified international call is not automatically fraudulent.
Review your outbound number inventory, keep authorization records current, and notify your provider when your calling setup changes. Monitor reports of blocked or mislabeled calls and investigate specific examples. Recheck authentication when adding a dialer, changing providers, or connecting a new contact center platform.