Customer Experience
 Blog
 Business Communication
 Leadership
 Marketing & Sales
 Nextiva News
 Productivity
 VoIP


A PCI call center is a contact center that handles payment card information and must follow the Payment Card Industry Data Security Standard (PCI DSS). Call center PCI compliance means protecting cardholder data throughout payment interactions, including phone calls, recordings, agent desktops, and payment systems. It requires secure processes, appropriate technology, and ongoing security controls.
If your agents accept credit card payments over the phone, compliance involves more than encrypting calls or using a payment gateway. You need to understand where payment data travels, who can access it, and which systems fall within PCI DSS scope.
This guide explains the current PCI DSS requirements, common call center security risks, and practical steps for handling customer payments securely.
What Is PCI Compliance for Call Centers?
Call center PCI compliance means meeting the Payment Card Industry Data Security Standard (PCI DSS) requirements that apply to your organization’s payment processes, systems, and data. These requirements help protect cardholder information from unauthorized access, theft, and misuse.
PCI DSS applies to organizations that store, process, or transmit payment card data, as well as systems that could affect the security of that data.
For call centers, this can include:
- Phone systems and VoIP infrastructure carrying payment information
- Agent desktops and applications used to process payments
- Call recording and screen recording systems
- Payment gateways and interactive voice response (IVR) systems
- Customer relationship management (CRM) tools that store or expose payment data
- Third-party payment service providers
For example, if a customer reads their credit card number to an agent, the systems carrying or processing that information may fall within PCI DSS scope.
A secure payment workflow can reduce exposure by directing customers to enter their payment information through a protected payment channel rather than sharing it with agents.
Is PCI DSS compliance mandatory?
PCI DSS is an industry security standard established by major payment card brands. It is not, by itself, a universal law.
However, businesses accepting card payments are generally required to comply through their agreements with payment processors, acquiring banks, and card networks. Noncompliance can result in financial assessments, increased processing costs, restrictions, or loss of card acceptance privileges.
Depending on the circumstances, a data breach may also trigger obligations under applicable privacy and data protection laws.
PCI DSS 4.0.1 Requirements for Call Centers
PCI DSS v4.0.1 is the current version of the Payment Card Industry Data Security Standard. It establishes technical and operational safeguards for organizations handling payment account information. The updated framework includes requirements that became effective on March 31, 2025, making them particularly relevant to compliance programs in 2026.
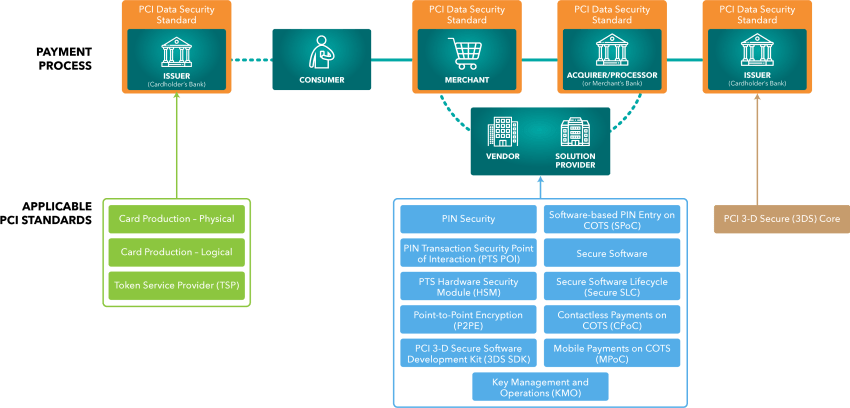
Although PCI DSS contains 12 principal requirements, call center managers should pay particular attention to these areas.
Protect stored payment information
Avoid retaining payment card data unless there’s a legitimate business need and an applicable PCI DSS requirement permits it.
Cardholder data, such as the primary account number (PAN), must be protected when stored. Sensitive authentication data, including card verification codes (CVV/CVC), must not be retained after authorization, even if encrypted. This applies to data captured in call recordings, transcripts, CRM notes, and other storage systems.
Encrypt payment data in transit
Protect payment card information when transmitted over open, public networks using strong cryptography and secure protocols. Remember that encrypting a VoIP connection does not automatically make the entire call center compliant. Other systems and processes handling card data may still fall within PCI DSS scope.

Restrict access to sensitive information
Limit access to payment systems and data based on job responsibilities and business needs. Use role-based permissions, appropriate authentication controls, and activity logging to reduce unauthorized access.
Monitor systems and maintain security controls
Maintain secure configurations, address software vulnerabilities, monitor relevant activity, and conduct required security testing. Call centers should work closely with IT and security teams to keep their communication systems and payment infrastructure secure.
Train employees to handle payments securely
Agents must understand the approved payment process and know what to do when customers share card details unexpectedly. Training should cover secure payment collection, prohibited storage practices, suspicious activity, and incident reporting.
Important: PCI DSS compliance applies to the complete payment environment. Using software advertised as PCI compliant does not automatically make every customer deployment compliant.
PCI Compliance Levels and Validation
PCI compliance levels help payment brands and acquiring banks determine how merchants must validate their adherence to PCI DSS. The validation requirements depend on factors such as the yearly volume of payment card transactions, the card brand, payment channel, and risk profile.
While merchant levels are commonly described as Levels 1 through 4, the structure and criteria are not identical across all payment brands.
| Validation approach | What it involves |
|---|---|
| Report on Compliance (ROC) | A detailed assessment, typically associated with higher-volume merchants or entities required to undergo formal evaluation |
| Self-Assessment Questionnaire (SAQ) | A structured assessment available to eligible organizations, with different versions based on payment processing arrangements |
| Attestation of Compliance (AOC) | Documentation supporting the organization’s assessment and compliance status |
| External vulnerability scanning | Required for applicable environments, using an Approved Scanning Vendor where specified |
For example, a business using a fully outsourced payment solution may have different validation requirements from a call center where agents manually enter card numbers into a payment application.
Your acquiring bank or payment processor should confirm the applicable merchant level and validation process. For more complex environments, consult a Qualified Security Assessor (QSA).
The key takeaway is that PCI requirements depend on how your business handles payment information—not simply how many agents work in your contact center.
Common PCI Compliance Risks in Call Centers
Call centers handle sensitive customer information through multiple systems and interactions. Even routine activities can introduce risk when payment data isn’t properly protected.
1. Writing down or storing payment information
Agents may record card details in notebooks, spreadsheets, CRM fields, or internal chat messages to complete transactions more quickly. These practices can expose sensitive information and expand the systems subject to PCI DSS requirements.
Use approved payment collection tools rather than unstructured notes or applications not designed to handle payment data.
2. Capturing card details in call recordings
If customers read their card numbers or CVVs aloud, recordings may capture information that should not be retained. This can create compliance problems even when the recording is stored in an encrypted system. Organizations need appropriate recording controls that prevent prohibited payment information from being retained.
3. Sharing payment details through insecure channels
Customers may send card information through email, SMS, live chat, or screenshots when trying to complete a payment. These channels can introduce additional systems into the PCI DSS scope. Agents should guide customers toward approved payment methods rather than requesting card details through unsupported channels.

4. Exposing card information on agent screens
Payment details displayed in applications or captured by screen recording tools may be accessible to unauthorized personnel. Secure workflows should limit agent visibility into sensitive payment information and prevent unnecessary collection or storage.
5. Unsecured remote working environments
Remote agents may work on personal networks, shared devices, or systems with insufficient security controls. Businesses need appropriate authentication, endpoint protection, access restrictions, and remote working policies for environments that handle payment information.
How To Process Card Payments Securely
Secure payment processing protects customer information while helping call centers handle transactions efficiently. Several technologies can reduce cardholder data exposure, although each has different capabilities and compliance implications.
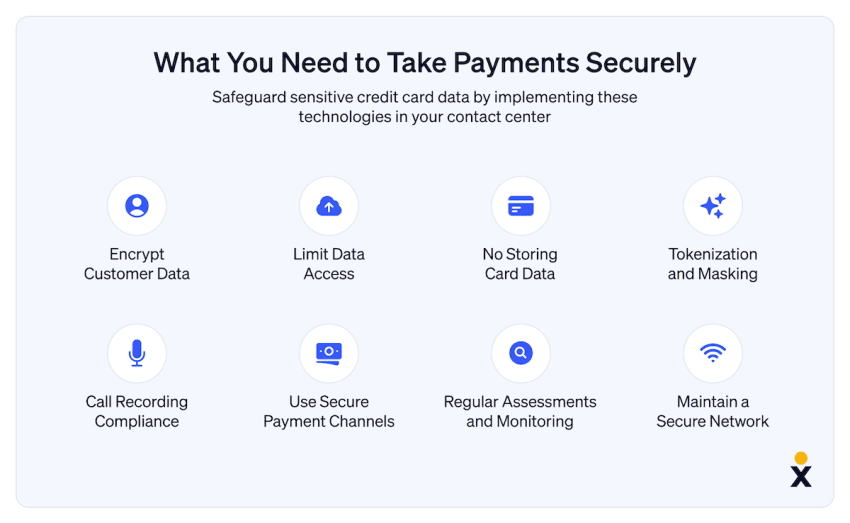
Secure IVR payments
A secure interactive voice response (IVR) system allows customers to enter payment details through an automated process. For example, an agent can transfer a customer to a payment IVR and receive confirmation when the transaction is complete.
Properly designed IVR workflows can keep sensitive card data away from the agent, but the exact PCI DSS scope depends on how the telephony and payment infrastructure is configured.
DTMF masking and suppression
Dual-tone multi-frequency (DTMF) technology generates tones when callers enter digits on their telephone keypad. DTMF masking or suppression can prevent audible tones from exposing card information during payment collection.
However, not every keypad-based payment system provides equivalent protection. Confirm how the technology handles, routes, and protects payment data throughout the transaction.
Tokenization
Tokenization replaces sensitive payment data with a substitute value called a token. Businesses can use tokens for supported follow-up processes without exposing the original card number to every connected application. The original payment information is handled within the authorized payment environment.
Tokenization can reduce exposure, but it doesn’t automatically remove every system or process from PCI DSS scope.
Payment gateways and agent-assisted payments
A secure payment gateway processes card transactions through designated payment infrastructure.
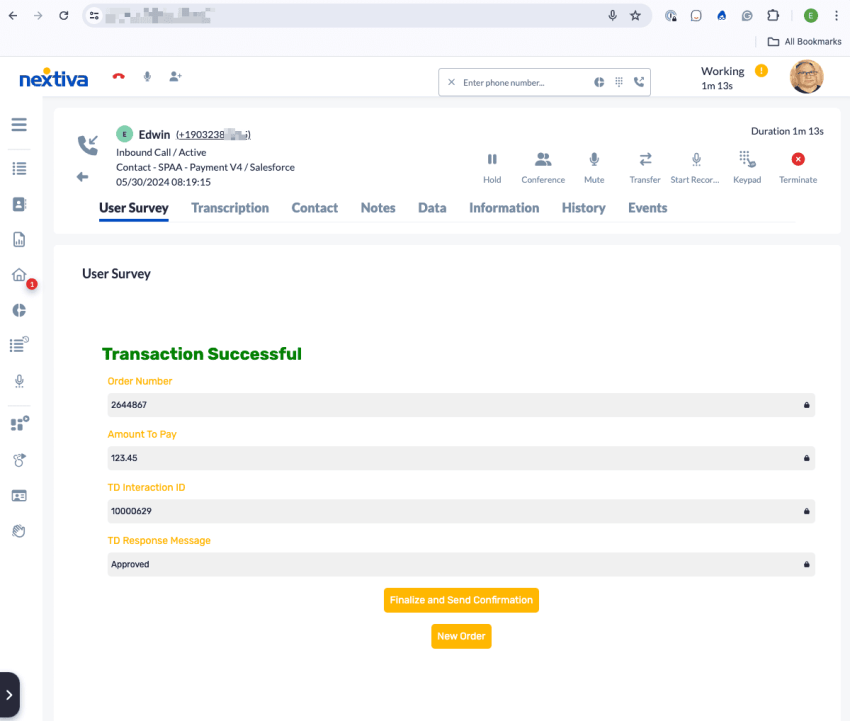
Some contact center solutions support agent-assisted payment workflows in which agents initiate a transaction, customers enter their card details through a secure channel, and agents receive the transaction status without accessing the card information.
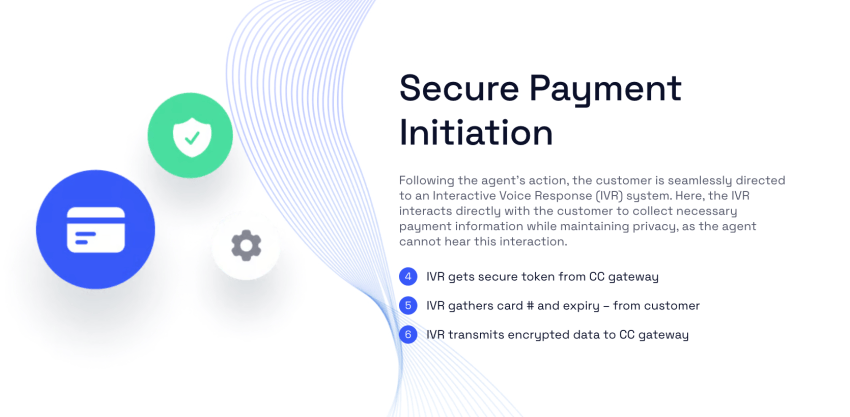
These workflows can reduce handling risks while maintaining a convenient customer experience.
PCI Compliance and Call Recording Rules
Call recording is valuable for training, quality assurance, and dispute resolution. But recording payment card information introduces additional PCI DSS considerations. Under PCI DSS, sensitive authentication data such as CVV/CVC values must not be stored after authorization, even if encrypted.
Call centers therefore need processes that prevent prohibited payment information from being retained in audio recordings, screen recordings, transcripts, or related systems.
Does pausing call recording ensure PCI compliance?
Pause-and-resume recording can help prevent payment information from being captured.
For example, an agent might pause recording before collecting payment details and resume afterward.
However, this does not automatically remove the agent’s workstation, telephone system, or other payment-handling components from PCI DSS scope. Manual recording controls also introduce the risk that an agent forgets to pause or resumes recording too early.
Better approaches to secure recording
Depending on your payment workflow, consider:
- Automated recording suppression during payment collection
- DTMF masking or suppression technologies
- Secure IVR payment handoffs
- Appropriate screen recording controls
- Restricted access to permitted recordings and transcripts
- Documented retention and deletion policies
The most suitable controls depend on your systems and the way customer card information flows through them. Please review your recording setup with your security team or PCI assessor, rather than assuming that one recording feature is sufficient for compliance.
Call Center PCI Compliance Checklist
Use this checklist to review your organization’s payment processes and identify areas that need attention.
1. Map the payment data flow
Document where customers provide card information and how it travels through your telephone systems, applications, networks, and payment processors. Identify which components store, process, transmit, or could affect the security of payment data.
2. Minimize cardholder data exposure
Avoid collecting or retaining payment data unnecessarily. Where appropriate, use secure IVR systems, agent-assisted payments, tokenization, and other safeguards to reduce the number of people and systems handling sensitive information.
3. Protect call and screen recordings
Configure controls to prevent prohibited authentication data from being stored. Review recording settings, transcripts, access permissions, retention policies, and payment workflows.
4. Implement strong access controls
Use appropriate authentication, role-based access, account management, and monitoring for systems handling cardholder data. Ensure agents and supervisors only access the information required for their responsibilities.
5. Secure remote and on-site environments
Work with IT teams to maintain secure endpoints, networks, configurations, and access controls. Establish clear policies for remote agents who handle payment-related interactions.
6. Assess third-party providers
Review the payment processors, contact center vendors, and other service providers involved in handling cardholder information. Request relevant compliance documentation and clarify responsibility for applicable PCI DSS controls.
7. Train agents regularly
Teach employees how to handle customer payments securely, recognize suspicious activity, and respond to incidents. Include refresher training when payment workflows, software, or policies change.
8. Conduct required assessments and security testing
Review your PCI DSS scope and validation requirements with your acquiring bank, payment processor, or QSA. Perform applicable vulnerability scanning, security testing, monitoring, and periodic reviews.
9. Maintain documentation and incident response procedures
Document payment workflows, applicable security controls, training, vendor responsibilities, and assessment results. Maintain an incident response process so employees know how to report and escalate potential payment data exposure.
Remember: This checklist is a practical starting point, not a substitute for a complete PCI DSS assessment.
How PCI Compliance Affects Customer Experience
PCI compliance isn’t just a security issue. The way businesses collect payments also affects how customers experience service.
An overly complicated process may require customers to repeat information, switch between applications, or spend additional time completing transactions. A well-designed payment workflow can protect sensitive information while keeping the conversation moving.
For example, an agent can help a customer resolve a billing question and then initiate a secure payment process. The customer enters card details without sharing them with the agent, and the agent receives confirmation when the transaction finishes.
For support teams, this approach can reduce manual handling of sensitive data while helping maintain an efficient customer experience. The goal is to make security an integral part of the service workflow rather than an additional obstacle for customers.
Simplify Contact Center Payments With Nextiva
Maintaining PCI compliance requires the right combination of technology, processes, employee training, and ongoing oversight.
Nextiva Contact Center helps businesses manage customer interactions across voice and digital channels through a unified platform. For payment collection, Nextiva also offers Secure Payment Agent Assist, a solution designed to support PCI-compliant payment workflows.
Secure Payment Agent Assist provides capabilities such as:
- Automated payment handoff: Transfer customers from agents to an IVR payment process.
- Secure payment entry: Allow customers to enter card details without speaking them to the agent.
- Agent reconnection: Return customers to the agent after payment completion.
- Payment status updates: Give agents visibility into transaction progress without exposing sensitive card details.
- Payment gateway connectivity: Support payment processing through compatible gateways.
These capabilities can help reduce agent exposure to payment information. However, your organization’s PCI DSS compliance still depends on the complete payment environment and applicable controls.
Ready to manage customer conversations and payments more securely?
Explore Nextiva Contact Center to see how unified communications and secure payment workflows can support your service operations.
Call Center PCI Compliance FAQs
PCI compliance means following applicable PCI DSS requirements when your call center handles payment card information. These requirements cover security controls for systems, employees, payment workflows, and third-party providers involved in processing or protecting cardholder data.
Yes, when recordings contain payment card data, applicable PCI DSS requirements may apply. Sensitive authentication data such as CVV values must not be stored after authorization, even if encrypted. Call centers should use appropriate technology and processes to prevent prohibited data from being retained.
Yes. Agents can assist customers with phone payments, but the payment process must meet applicable PCI DSS requirements. Secure IVR systems and agent-assisted payment solutions can help reduce exposure by allowing customers to enter card details without sharing them directly with agents.
No. Pausing recordings can prevent sensitive payment information from being stored, but it does not automatically address the security of agent desktops, telephone infrastructure, payment applications, or other systems within PCI DSS scope.
PCI DSS v4.0.1 is the current version. It was published in June 2024, and the new requirements initially scheduled for March 31, 2025, are now effective. Organizations should use the current standard when planning assessments and controls.
Not automatically. A compliant payment processor may reduce the amount of cardholder data handled by your organization; however, you remain responsible for applicable PCI DSS requirements. The exact scope depends on your payment workflows, systems, and vendor responsibilities.
Consequences can include payment-brand assessments, increased processing costs, contractual penalties, restrictions on card processing, and potential liability following a data breach. The financial impact varies based on the situation, affected parties, and applicable agreements.